Tag: User Protection Fund

  • Swiss Bank Shields Bitget Institutional Clients as Retail Funds Remain Frozen

    Swiss Bank Shields Bitget Institutional Clients as Retail Funds Remain Frozen

    Key Highlights

    • Bitget confirmed a Sept. 24 wallet breach that transferred approximately $387.5 million in assets to attacker-controlled addresses, affecting hot and warm wallet layers while cold wallets remained secure.
    • Sygnum Bank’s Protect service offers Bitget institutional clients an off-exchange custody route where pledged collateral—including Bitcoin, Ethereum, stablecoins, and U.S. Treasuries—is held in segregated, bankruptcy-remote Swiss accounts, reducing direct exposure to exchange wallets.
    • Withdrawals remain suspended as of Sept. 25; Bitget cites a User Protection Fund holding 5,500 BTC (valued above $464 million at the time of the breach) to cover qualifying losses, with a withdrawal-status update promised by Sept. 26 04:00 UTC.

    The Breach and Immediate Response

    Bitget detected unauthorized transfers at 18:31 UTC on Sept. 24, initially estimating the loss at roughly $351.6 million. A Sept. 25 update raised that figure to approximately $387.5 million after a fuller accounting that included Zcash and TRON transfers; the exchange emphasized the revision did not represent a fresh wave of unauthorized activity. Bitget stated the breach reached portions of its hot and warm wallet layers while cold wallets remained secure. The exchange said it identified and remediated the underlying vulnerability, contained the incident, and engaged Mandiant and SlowMist to assist the investigation.

    Withdrawals were paused immediately, with deposits and trading left operational. Bitget’s notice promised to announce a withdrawal plan or status by Sept. 26 at 04:00 UTC. For ordinary customers, a displayed balance and the ability to trade do not by themselves provide an exit while withdrawals are unavailable.

    Sygnum’s Off-Exchange Custody Alternative

    On the same day as the breach, Sygnum announced that Bitget’s institutional clients could trade against collateral held at the Swiss bank instead of placing that collateral in Bitget’s wallets. Under the Protect service, eligible clients onboard with Sygnum, sign a contractual framework, open a Protect portfolio, and pledge assets—Bitcoin, Ethereum, stablecoins, and U.S. Treasuries are listed as eligible collateral—before receiving exchange margin. Bitget mirrors the balance as trading margin.

    Sygnum describes the collateral as held in segregated accounts off the bank’s balance sheet and bankruptcy remote under Swiss banking law. The arrangement is intended to keep pledged assets outside Bitget’s estate should the exchange face financial distress, and to reduce direct custody exposure to Bitget’s own wallets. The announcement is dated Sept. 24 but does not state when client access became operational, whether the integration preceded or followed the 18:31 UTC breach, how many Bitget clients have onboarded, any Bitget-specific collateral balance, or whether Sygnum-held assets were involved in the incident. Public figures for Protect’s total assets and the trading-volume share of all integrated exchanges do not measure Bitget client uptake.

    User Protection Fund and Recovery Outlook

    For users holding ordinary balances on Bitget, the exchange pointed to its User Protection Fund. In its initial Sept. 24 notice, Bitget said the fund was worth more than $464 million and that the then-estimated $351.6 million incident fell within its coverage. The fund’s public page lists 5,500 BTC and states users may claim for qualifying losses from platform-wide events beyond their own actions or trading behavior, with Bitget reserving the right to assess and investigate claims. The dollar value of the Bitcoin-denominated fund moves with BTC’s price; Bitget’s August report put the fund’s monthly average at $382 million and its month-end value near $432 million on the same 5,500 BTC holding.

    Bitget also said it froze some affected assets through work with industry partners, but its Sept. 25 update did not quantify the frozen or recovered amount. The next measurable tests are a confirmed withdrawal timetable, a firmer loss and recovery accounting, and the terms of any fund disbursement.

    Why This Matters

    The incident highlights a structural tension in crypto custody: even when institutional collateral is segregated off-exchange with a regulated bank like Sygnum, trading still depends on the exchange’s order, margin, and settlement processes. Public materials do not establish that a Protect client can instantly reclaim pledged collateral during an exchange disruption, nor that operational problems could never delay settlement. Conversely, they do not show that any Sygnum client is blocked from its collateral in this incident. The arrangement creates an optional boundary between institutional collateral and Bitget wallet custody—Bitget’s ordinary balances faced exchange-wallet exposure, while Institutional Protect keeps pledged collateral off-exchange with Sygnum. Missing facts include Bitget-specific Protect uptake and the contract terms governing collateral release and settlement when the exchange is under strain.

    Frequently Asked Questions

    How much was stolen in the Bitget breach and which wallets were affected?

    Bitget estimates approximately $387.5 million in assets were transferred to attacker-controlled addresses. The breach reached hot and warm wallet layers; cold wallets were not compromised.

    What is Sygnum Protect and how does it differ from keeping funds on Bitget?

    Sygnum Protect lets eligible institutional clients pledge collateral—such as Bitcoin, Ethereum, stablecoins, and U.S. Treasuries—in segregated, bankruptcy-remote accounts at the Swiss bank. Bitget mirrors that collateral as trading margin, but the assets remain off Bitget’s balance sheet and outside its wallets, reducing direct custody exposure.

    When will Bitget withdrawals resume and are user funds insured?

    Withdrawals remain suspended as of Sept. 25. Bitget promised an update by Sept. 26 04:00 UTC. The exchange cites a User Protection Fund holding 5,500 BTC (valued above $464 million at the time of the breach) to cover qualifying platform-wide losses, subject to claim assessment and investigation.
  • Circle and Tether Freeze Hacker Wallet After Massive Bitget Crypto Heist

    Circle and Tether Freeze Hacker Wallet After Massive Bitget Crypto Heist

    Key Highlights

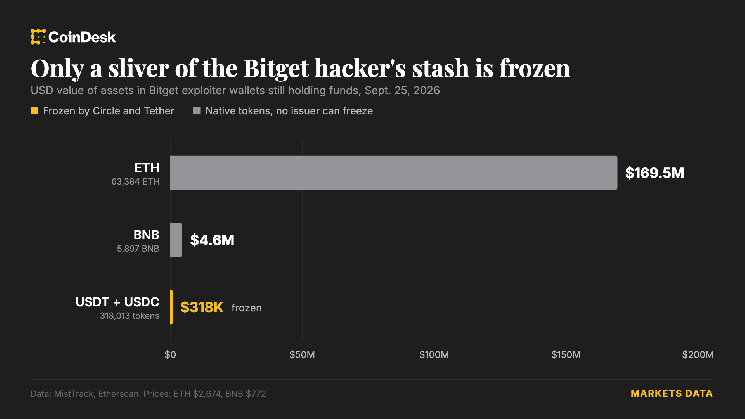
    • Circle and Tether froze approximately $318,000 in stablecoins (218,023 USDT and 99,990 USDC) held in a wallet labeled “Bitget Exploiter 8” on Etherscan, linked to Thursday’s $351.6 million Bitget exchange hack.
    • The frozen assets represent a small fraction of the total haul; blockchain analytics firm MistTrack confirms other exploiter addresses still hold over 63,000 ETH (valued at roughly $200 million+), which no issuer can freeze because they are native ether, not permissioned stablecoins.
    • Bitget CEO Gracy Chen stated the breach stemmed from a compromised backend system in the exchange’s wallet infrastructure that allowed attackers to spoof transaction data and trigger the authorization process, ruling out a private key compromise. She confirmed the exchange’s $464 million user protection fund covers the loss.

    Rapid Stablecoin Freeze by Circle and Tether

    Circle moved swiftly to blacklist the Ethereum address tagged as “Bitget Exploiter 8” at 05:00 UTC on Friday, according to onchain data. The wallet contained 170.47 ETH, 218,023 USDT, and 99,990 USDC at the time of the freeze. Blockchain security firm MistTrack reported that Tether subsequently banned the same wallet, effectively immobilizing the USDT and USDC balances—totaling roughly $318,000. While the action demonstrates the ability of centralized stablecoin issuers to intervene when funds hit permissioned tokens, the vast majority of the stolen assets remain in ether, which operates without a central freeze mechanism.

    Breach Mechanics: Backend Compromise, Not Private Key Theft

    Bitget CEO Gracy Chen provided a technical post-mortem, explaining that attackers compromised a backend system in the exchange’s wallet infrastructure, spoofed transaction data and triggered its authorization process to move funds out. Chen explicitly ruled out a private key compromise, distinguishing this incident from typical hot-wallet private key thefts. She added that Bitget’s user protection fund, which holds over $464 million, covers the loss, aiming to reassure users that deposits remain fully backed.

    Contrast with April’s Drift Protocol Incident

    The response stands in sharp contrast to Circle’s handling of the April $285 million Drift hack, where the attacker moved about $232 million in USDC from Solana to Ethereum using Circle’s own cross-chain transfer protocol. At the time, critics including onchain investigator ZachXBT argued Circle could have moved faster to blacklist wallets and freeze funds. Circle maintained that it freezes assets when legally required, underscoring the regulatory and procedural constraints that govern stablecoin issuers’ intervention policies.

    Why This Matters

    The Bitget hack highlights the persistent vulnerability of centralized exchange infrastructure—specifically backend authorization layers—even when private keys remain secure. It also illustrates the asymmetric power of stablecoin issuers: they can neutralize a portion of stolen funds once they touch USDC or USDT, but they have no control over native assets like ETH. For the broader crypto market, the incident reinforces the importance of exchange solvency reserves and user protection funds, while reigniting debate over the speed and transparency of stablecoin freeze decisions in the absence of uniform legal mandates.

    Frequently Asked Questions

    How much of the stolen $351.6 million has been frozen?
    Only about $318,000—comprising 218,023 USDT and 99,990 USDC—has been frozen. The remaining assets, primarily over 63,000 ETH held in other exploiter wallets, cannot be frozen by any issuer.
    What caused the Bitget security breach?
    According to CEO Gracy Chen, attackers compromised a backend system in the exchange’s wallet infrastructure, spoofed transaction data, and triggered the authorization process to withdraw funds. A private key compromise was explicitly ruled out.
    Will Bitget users lose funds?
    Bitget says no. The exchange’s user protection fund holds over $464 million, which CEO Gracy Chen confirmed is sufficient to cover the entire $351.6 million loss.
  • Bitget Freezes Withdrawals After $351.6M Hack

    Bitget Freezes Withdrawals After $351.6M Hack

    Key Highlights

    • Bitget confirmed a $351.6 million exploit from its hot wallets on September 24, 2026, with on-chain data showing the first unauthorized transfer at 18:31:11 UTC and major outflows continuing for nearly three hours before the public notice.
    • The attacker rapidly converted freezable stablecoins (USDT, USDC, Tether Gold) into ether via a router contract, paying up to 5% above spot price, suggesting a deliberate race against issuer freeze functions.
    • CEO Gracy Chen stated user funds are safe and the loss is covered by Bitget’s $464 million User Protection Fund, while withdrawals remain suspended pending a full incident report due within 24 hours.

    Timeline Reveals Hours-Long Gap Between Detection and Containment

    Bitget chief executive Gracy Chen confirmed on Thursday night that attackers drained roughly $351.6 million from the exchange’s hot wallets, suspending customer withdrawals while an investigation proceeds. Chen published the notice at 21:30 UTC on September 24, 2026, stating: “At 18:31 UTC on September 24, 2026, Bitget’s security systems detected unauthorized transfers from some of our hot wallets. Our security team activated emergency response protocols immediately.”

    On-chain data corroborates the 18:31 detection timestamp but paints a more granular picture of the subsequent three hours. At 18:31:11 UTC, a wallet labeled “Bitget 6” on Etherscan, Arbiscan, and BscScan sent 0.84 ether to a newly created address — a test transaction that typically precedes large transfers and marks the first movement of the breach. The outflows accelerated rapidly: by 18:58:59, the same wallet moved 34,751,168 USDT; at 19:01:20 on Arbitrum, 19,668,851 USDT0; at 19:01:23, 12,852,046 USDC; and at 19:01:35, 7,130.86 ether. A second wallet, “Bitget 35,” added 15,362 ether across three transfers, followed by another 223.2 ether at 21:23:11 — two hours and 52 minutes after detection and just seven minutes before Chen’s public notice.

    Across Ethereum and Arbitrum alone, $133.4 million exited Bitget-labeled wallets, plus 3,000 Tether Gold tokens worth approximately $12.8 million from a third address. The remainder of the $351.6 million moved on other chains. Chen emphasized that cold storage was never touched and described a three-tier wallet architecture in which “the breach contained only a portion of the hot wallet and warm wallet layers.” However, the extended window between detection and containment allowed substantial value to leave the exchange’s control.

    Attacker Strategy Signals Intent to Outrun Freeze Functions

    The composition of stolen assets and the speed of conversion provide the clearest signal of the attacker’s intent. Tether can freeze USDT, Circle can freeze USDC, and Tether can freeze its gold token — but ether cannot be frozen by any central party. Within six minutes of receiving the stablecoins, the attacker pushed all three asset types into router contract 0x7c96279E, which fanned them across Uniswap V3 pools and the Uniswap V4 PoolManager, converting everything into ether.

    Pseudonymous analyst DCF GOD, who identified the Arbitrum leg before Bitget’s public statement, noted the buyer was “paying up to +5% over spot” and drove one pool to $2,870 against a spot price near $2,688. “which makes no sense if someone was just trying to buy eth,” he wrote. The premium paid aligns with a seller racing issuer freeze functions rather than a typical market participant. The resulting ether — approximately 24,590 ETH — now sits in three previously inactive wallets: 10,000 ETH at 20:13, another 10,000 at 20:19, and 4,590 more at 21:41:11. That final transfer occurred ten minutes after Chen’s notice and one minute after Bitget’s official account stated it had “identified and flagged the relevant transfer addresses.”

    Exchange Response and Industry Context

    “User funds are safe,” Chen wrote. “The full amount of this loss falls within the coverage of Bitget’s User Protection Fund, which currently holds over $464 million.” She added that deposits and trading continue normally and promised a full incident report within 24 hours: “We will not speculate on the attack vector until the investigation is complete.”

    That restraint reflects a pattern security experts recognize across recent major exchange breaches. Ido Sofer, founder and CEO of key management firm Sodot, described the dynamic on the On The Margin podcast: “Those are off-chain hacks that led to on-chain loss of funds. Developer credentials, deployment keys, API keys that are being stolen. And that provided access to moving funds on chain.” His blunter assessment: “There will be hacks. The question is, is it gonna be in your company or not?”

    Bitget’s $464 million protection fund against a $351.6 million loss provides a thin but real cushion. The exchange has published proof-of-reserves attestations for 45 consecutive months, most recently reporting a 122% reserve ratio for August. The immediate test is whether withdrawals reopen without disruption.

    Why This Matters

    This incident represents the largest exchange loss since the Bybit breach and follows a series of high-profile security failures including the $130 million Coldcard theft and a $137 million November exploit that reshaped DeFi’s yield infrastructure. The attack underscores a persistent industry vulnerability: custodial exchanges remain prime targets where compromised off-chain credentials — developer keys, API access, deployment infrastructure — translate directly into on-chain asset drainage. The attacker’s sophisticated conversion strategy, deliberately overpaying to swap freezable assets for censorship-resistant ether before issuers could intervene, demonstrates an evolving playbook that prioritizes speed and asset selection over stealth. For the broader market, the episode tests whether exchange-backed protection funds can credibly absorb nine-figure losses without contagion, and whether proof-of-reserves attestations translate into operational resilience when withdrawals are suspended. The 24,590 ether now parked in three fresh wallets remains a live threat vector; any movement will signal the next phase of laundering or liquidation.

    Frequently Asked Questions

    What assets were stolen and how much is the total loss?
    Approximately $351.6 million was drained from Bitget’s hot wallets across multiple chains. On Ethereum and Arbitrum alone, $133.4 million in USDT, USDC, USDT0, and ether left labeled wallets, plus 3,000 Tether Gold tokens worth ~$12.8 million. The remainder moved on other networks. The attacker converted all freezable stablecoins and gold tokens into ether within minutes.
    Are user funds affected and will withdrawals resume?
    CEO Gracy Chen stated “User funds are safe” and confirmed the loss falls within Bitget’s User Protection Fund, which holds over $464 million. Cold storage was not touched. Deposits and trading continue normally, but withdrawals remain suspended pending investigation. A full incident report is promised within 24 hours from the September 24 notice.
    How did the attacker move the funds and can they be recovered?
    The attacker used a router contract (0x7c96279E) to swap USDT, USDC, and Tether Gold for ether via Uniswap V3 and V4 pools, paying up to 5% above spot price to execute quickly before issuers could freeze the stablecoins. The resulting ~24,590 ether now sits in three previously unused wallets. Ether cannot be frozen by any central party. Tether and Circle have freeze capabilities for USDT and USDC respectively, but those assets were already converted. Recovery depends on law enforcement action, exchange cooperation, and whether the attacker makes operational security mistakes when moving the ether.
  • Bitget CEO Confirms Hack, Reveals Massive Losses; Withdrawals Suspended

    Bitget CEO Confirms Hack, Reveals Massive Losses; Withdrawals Suspended

    Key Highlights

    • Cryptocurrency exchange Bitget detected unauthorized transfers from hot wallets totaling approximately $351.6 million on September 24, 2026, at 18:31 UTC.
    • Cold wallets remain secure and the loss is fully covered by Bitget’s User Protection Fund, which holds over $464 million in assets.
    • Withdrawals are temporarily suspended as a precaution; deposits and trading continue normally with hourly updates promised and a full incident report due within 24 hours.

    Breach Detection and Emergency Response

    Cryptocurrency exchange Bitget released an official statement on September 24, 2026, confirming that its security systems detected unauthorized transfers from several hot wallets at 6:31 PM UTC. According to a statement by Bitget CEO Gracy Chen, the company’s security team activated emergency response protocols immediately upon detection. The exchange announced that its emergency response team was activated within minutes, the addresses where the unusual transfers occurred were identified and marked, and relevant parties were notified. Law enforcement and security companies have been officially involved in the investigation process.

    [SECURITY NOTICE] Bitget Hot Wallet Incident — September 24, 2026
    At 18:31 UTC on September 24, 2026, Bitget’s security systems detected unauthorized transfers from some of our hot wallets. Our security team activated emergency response protocols immediately.
    What we have…
    — Gracy Chen @Bitget (@GracyBitget) September 24, 2026

    Wallet Architecture Limits Impact

    Bitget emphasized that the incident was limited to only a portion of the hot and warm wallet layers. The company operates a three-layered wallet architecture, and cold wallets were not affected by the breach. This structural segregation prevented the compromise from extending to the majority of user funds held in offline storage. The exchange maintained that account balances are accurate and user assets are protected despite the hot wallet losses.

    User Protection Fund Coverage

    The company stated that the entire approximately $351.6 million loss could be covered by Bitget’s User Protection Fund, which holds over $464 million in assets. This reserve mechanism is designed to absorb losses from security incidents without impacting individual user holdings. Bitget reiterated that user funds are safe and the protection fund has sufficient capacity to cover the full extent of the unauthorized transfers.

    Operational Status and Next Steps

    As a precautionary measure while a security review is underway, Bitget has temporarily suspended withdrawal transactions. However, deposits and trading continue as normal. The exchange announced that withdrawals will be reopened after the security review is complete. The company committed to sharing updates on the incident hourly and publishing a comprehensive incident report detailing the cause of the attack, the method used, and corrective measures taken within 24 hours. The method used in the attack has not been disclosed at this stage, and Bitget stated it will not speculate on the attack vector until the investigation is complete.

    Why This Matters

    The Bitget incident highlights the persistent security challenges facing centralized cryptocurrency exchanges, particularly regarding hot wallet management. Hot wallets, which remain connected to the internet to facilitate rapid withdrawals and trading operations, represent a concentrated attack surface. The exchange’s three-layered architecture—segregating cold, warm, and hot wallets—demonstrates a defense-in-depth approach that successfully contained the breach to the most exposed layer. The existence of a substantial User Protection Fund, capitalized at over $464 million, reflects an industry trend toward self-insurance mechanisms that can absorb losses without requiring bailouts or socialized loss distribution among users. The temporary withdrawal suspension, while disruptive, follows standard incident response protocols to prevent further outflows during forensic analysis. The promised transparency—hourly updates and a detailed post-mortem within 24 hours—sets a benchmark for crisis communication in the digital asset sector. Regulators and industry observers will likely scrutinize the attack vector once disclosed, as it may inform evolving security standards for custodial platforms.

    Frequently Asked Questions

    Are user funds on Bitget safe after this incident?

    Yes. Bitget has confirmed that cold wallets were not affected and the approximately $351.6 million loss is fully covered by its User Protection Fund, which holds over $464 million in assets. Account balances remain accurate and user assets are protected.

    Can I still trade and deposit on Bitget?

    Yes. Deposits and trading continue as normal. Only withdrawal transactions have been temporarily suspended as a precautionary measure while the security review is conducted.

    When will withdrawals resume and when will we know how the attack happened?

    Bitget states withdrawals will reopen after the security review is complete. The company will provide hourly updates and publish a comprehensive incident report detailing the cause, method, and corrective measures within 24 hours of the initial detection.