Tag: Smart contract vulnerability

  • Fetch.ai Investigates Token Conversion Contract Exploit

    Fetch.ai Investigates Token Conversion Contract Exploit

    Key Highlights

    • Fetch.ai is actively investigating a reported exploit targeting its token conversion contract, prompting immediate security scrutiny.
    • The project’s official X account (@Fetch_ai) has warned users to rely exclusively on official communication channels for updates.
    • The incident has introduced uncertainty into Fetch.ai trading activity, with market participants awaiting investigation results.

    Fetch.ai Launches Investigation Into Token Conversion Contract Exploit Reports

    Fetch.ai, the decentralized platform leveraging artificial intelligence-driven agents for automation, has confirmed it is investigating reports of a security exploit involving its token conversion contract. The announcement, disseminated through the project’s official X account @Fetch_ai, marks a critical moment for the blockchain network as it confronts potential vulnerabilities in its core infrastructure. The development team’s proactive disclosure signals a commitment to transparency, though the situation has already cast a shadow over user confidence and market sentiment surrounding the FET token ecosystem.

    Official Channels Emphasized Amid Security Scrutiny

    In its public communication, Fetch.ai explicitly urged community members and token holders to trust only verified official channels for information regarding the ongoing investigation. This directive underscores the heightened risk of misinformation, phishing attempts, and social engineering attacks that typically proliferate during security incidents in the cryptocurrency space. The project’s emphasis on channel verification reflects broader industry best practices for incident response, where controlling the narrative and preventing scam exploitation are paramount to protecting the user base.

    Market Reaction Reflects Investor Apprehension

    Trading activity for Fetch.ai currently shows no reported volume or price data, a phenomenon that market observers attribute to the uncertainty generated by the exploit announcement. The absence of liquidity metrics suggests that investors and traders are adopting a wait-and-see posture, reluctant to commit capital until the scope and severity of the vulnerability are clarified. This trading pause highlights the acute sensitivity of digital asset markets to security-related news, particularly for protocols like Fetch.ai that position themselves at the intersection of blockchain and artificial intelligence infrastructure.

    Why This Matters: Security Trust in AI-Blockchain Convergence

    The Fetch.ai exploit investigation carries significance beyond a single protocol’s technical challenges. As a platform building at the convergence of decentralized ledger technology and autonomous AI agents, Fetch.ai represents a category of infrastructure where security assumptions are still being stress-tested in production environments. Token conversion contracts—critical bridges for asset interoperability—are high-value targets for attackers due to their liquidity concentration and complex logic. The outcome of this investigation will likely inform security standards across the emerging AI-agent blockchain sector, influencing how developers architect conversion mechanisms, how auditors assess multi-layer protocols, and how users evaluate risk in systems where autonomous agents execute financial transactions. Regulatory observers will also monitor the response, as incident handling transparency becomes a benchmark for consumer protection in decentralized finance.

    Frequently Asked Questions

    What specific component of Fetch.ai is under investigation?

    The investigation focuses on the project’s token conversion contract, a smart contract mechanism responsible for facilitating asset exchanges or migrations within the Fetch.ai ecosystem. No other protocol components have been implicated in the current reports.

    Where should users obtain verified updates about this situation?

    Fetch.ai has directed all community members to rely exclusively on its official communication channels, particularly its verified X account @Fetch_ai, for accurate and timely information regarding the investigation’s progress and any required user actions.

    Has the exploit affected FET token trading on exchanges?

    Current market data indicates no reported trading volume or price for Fetch.ai, suggesting that exchanges may have suspended trading or that market participants have withdrawn liquidity pending clarification of the security incident’s scope and resolution.
  • Hacker Turns 55 Days of Failed Transactions Into $3 Million Master Key Draining GalaChain Wallets

    Hacker Turns 55 Days of Failed Transactions Into $3 Million Master Key Draining GalaChain Wallets

    GalaChain August Exploit Reveals Signature Verification Flaw That Survived Multiple Audits

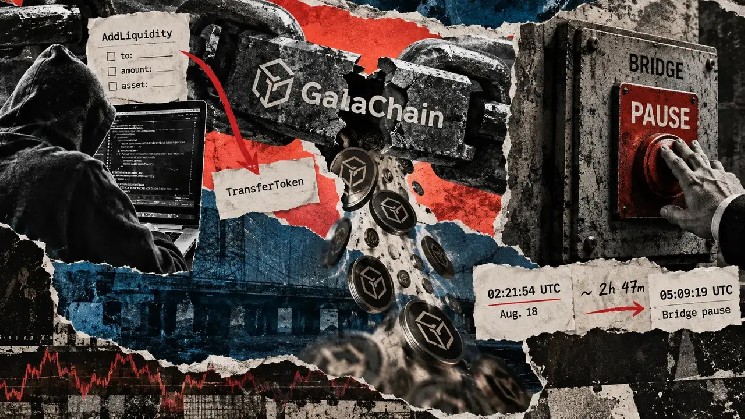
    A security breach on GalaChain in August exploited a novel vulnerability: failed transactions were converted into reusable authorization credentials, allowing an attacker to drain approximately 2 billion $GALA tokens—worth roughly $3 million at the time—along with dozens of other assets from nine wallets. The incident, detailed in a September 14 postmortem from Gala Games, exposes a critical gap in how blockchain systems validate signatures and protect against replay attacks, raising urgent questions about defense speed when exploitation becomes automated.

    Failed Transactions Became an Attack Inventory

    The attacker arrived prepared with 74 replayable signatures harvested from failed transactions dating back as far as 55 days, according to Gala. Those signatures were paired with what appears to be detailed knowledge of the targeted accounts. Of 59 account-token combinations attacked, 56 were drained for their exact balance on the first attempt. The four largest $GALA positions were taken in descending order within 18 seconds.

    That pattern strongly suggests reconnaissance occurred before exploitation began, rather than balances being discovered transaction-by-transaction during the attack. Execution then moved at machine speed: Gala recorded 1,066 submissions at a median interval of 4.5 seconds, with 73.9% arriving exactly one block apart.

    EIP-712 Verification Flaw Allowed Signature Scope Mismatch

    The historical signatures were valuable because of how GalaChain handled EIP-712 typed-data verification. Before the patch, the verifier accepted type definitions supplied with the request rather than deriving them from the invoked operation. This allowed a signature covering one set of fields to be presented while another method executed using additional information the signer had never committed to.

    One on-chain example shows a TransferToken call processing about 1.64 billion $GALA even though the EIP-712 structure supplied for verification described an AddLiquidity operation. The destination, quantity, and token instance used by the transfer were outside the signed structure. The signature itself was cryptographically valid, yet the system could not guarantee that the account holder had authorized the economic effects execution ultimately produced.

    Gala stated investigators found no evidence that affected users’ private keys, seed phrases, or passwords were compromised—a conclusion that relies partly on internal evidence the company has not published.

    Separate Replay Weakness Expanded the Attack Surface

    A second flaw in replay protection compounded the problem. GalaChain assigned unique transaction keys intended to stop the same signed payload from being submitted more than once. However, when a transaction failed, the key could roll back alongside the unsuccessful state changes. The signature remained visible on the public ledger while the replay key remained available for reuse.

    Gala reported that 57 of the 60 historical source transactions linked to the exploit contained at least one failed inner operation, while none completed entirely successfully. The combination effectively turned unsuccessful historical requests into reusable permissions. An attacker did not need to forge signatures or steal private keys behind every targeted wallet because authentic signatures had already been published on-chain.

    Audits Missed the Interaction Between Safeguards

    The vulnerability survived external security reviews before the attack. Gala said the relevant verification logic was examined during an authorization-focused CertiK engagement in late 2025 and an SDK review by Hashlock in January. Neither identified the signature-scope issue. The company has not published those reports, making it difficult to determine what each review tested or how extensively it examined the interaction between signature verification and replay protection.

    Notably, the replay mechanism itself was introduced after an earlier CertiK finding. That protection could prevent reuse after a transaction key had been consumed. The August 18 attacker found the boundary where the safeguard stopped applying: failed transactions whose signed payloads had become public while their unique keys remained unused.

    Patches Close the Technical Gaps, Not the Response-Time Problem

    Gala subsequently changed both systems. Signature verification now derives its type information from the operation being called rather than trusting a caller-supplied definition. Requests also include identifiers that bind signatures more closely to the channel, contract, and method being authorized, while expiration timestamps limit how long signed payloads remain valid. The replay fix persists a unique transaction key even if the underlying business operation fails, preventing the same historical request from remaining available for another attempt.

    Those patches close the two weaknesses described in the postmortem. They do not resolve the response-time problem that emerges once a valid-looking attack is already underway. The first verified unauthorized transfer occurred at 02:21:54 UTC. Gala paused the bridge at 05:09:19 UTC—about two hours and 47 minutes later—and began removing roles from the recipient address at 05:22 UTC. The company has not disclosed when its monitoring first detected the activity, so that interval cannot be treated as its reaction time. Gala said attempts to move assets out through the bridge were rejected after the pause.

    The chronology nevertheless shows the disparity facing operators once exploitation reaches machine speed: submissions can arrive every few seconds while detection, investigation, and emergency intervention may still require human decisions.

    Bridge Operators Face a Machine-Speed Defense Problem

    Gala said it has since added per-identity rate limits, behavioral monitoring for high-value accounts, and additional review for bridge withdrawals above certain thresholds. Those measures move security controls earlier in the settlement process, where unusual activity can be slowed before assets leave the system.

    They also introduce trade-offs. Operation-bound signatures, expirations, and replay keys largely enforce the instructions a user actually signed. Rate limits and behavioral triggers require operators to decide what constitutes abnormal activity, while withdrawal holds can delay legitimate users as well as malicious ones.

    Gala has described the attacker as using AI-assisted tooling, but that assessment relies on internal evidence the company has not released. That distinction matters as crypto firms increasingly frame security threats around artificial intelligence. For bridge operators, the more immediate issue is whether automated attackers can exploit valid-looking authorization paths faster than monitoring systems can identify and contain them.

    Investigation and Longer-Term Audit Implications

    Gala said it has filed a complaint with the FBI’s Internet Crime Complaint Center and sent preservation and freeze requests to platforms involved as it tracks proceeds across four chains. The longer-term challenge is now likely to shift toward audit scope. Reviews that test signature verification, replay protection, and transaction execution separately may miss vulnerabilities that appear only when those systems interact.

    For GalaChain, future audits will have to establish whether similar authorization gaps remain elsewhere in its SDK. For bridge operators more broadly, the commercial cost of relying on a human-triggered pause rises with every block once an attacker arrives with harvested signatures, mapped balances, and an automated submission engine.

  • Bithumb Places Altcoin on Delisting Watchlist, Explains Reasoning

    Bithumb Places Altcoin on Delisting Watchlist, Explains Reasoning

    Bithumb Places HEMI Token on Delisting Watchlist Following Smart Contract Security Vulnerability

    South Korean cryptocurrency exchange Bithumb has added the HEMI token to its delisting watchlist after a security vulnerability was identified in the smart contract responsible for the token’s initial reward distribution. The exchange announced the decision in an official statement, citing unauthorized asset liquidation stemming from the flaw.

    Smart Contract Flaw Triggers Unauthorized Withdrawals

    According to Bithumb’s statement, the vulnerability was discovered in the smart contract used by the organization operating the HEMI ecosystem to distribute initial reward claims. Due to this security issue, some tokens were withdrawn from the contract in an unusual manner, and assets were liquidated without authorization.

    The incident prompted Bithumb to re-evaluate the trading status of the HEMI token on its platform. As a precautionary measure, the exchange placed the token on its delisting watchlist and confirmed it will closely monitor further developments related to the project.

    Watchlist Status Does Not Guarantee Delisting

    Being added to the delisting watchlist does not mean HEMI has been permanently removed from Bithumb. Instead, this status indicates the token is under review to determine whether it continues to meet the exchange’s listing criteria. Trading support may be terminated in the future if the token fails to satisfy these requirements.

    Cryptocurrency exchanges typically re-evaluate listing status when projects experience security issues, critical smart contract vulnerabilities are discovered, or investor assets are placed at risk. Smart contract-related security incidents in particular pose significant risks to the security of user funds.

    Project Response Will Determine Future on Exchange

    Bithumb’s subsequent assessments will be crucial for HEMI’s future on the platform. Key factors in the review process will include:

    • The project’s response to the security vulnerability
    • How any resulting losses were handled
    • Measures implemented to prevent similar incidents from recurring

    Investors Advised to Monitor Official Announcements

    Investors holding HEMI tokens on Bithumb are expected to follow any new announcements from the exchange regarding the token’s status. The situation remains fluid, and further updates from both Bithumb and the HEMI project team will clarify the path forward.

    Disclaimer: This article is for informational purposes only and does not constitute investment advice.