Key Highlights
- Ethereum co-founder Vitalik Buterin reports that local AI models on high-end laptops, specifically Qwen 3.8 Flash running via llama.cpp, are approaching a practical turning point for handling a “large share” of daily computing tasks.
- September benchmarks on a Strix Halo laptop show input processing of 109.82–373.22 tokens per second and output generation of 18.42–33.37 tokens per second, marking a significant expansion from the narrower role Buterin described in April.
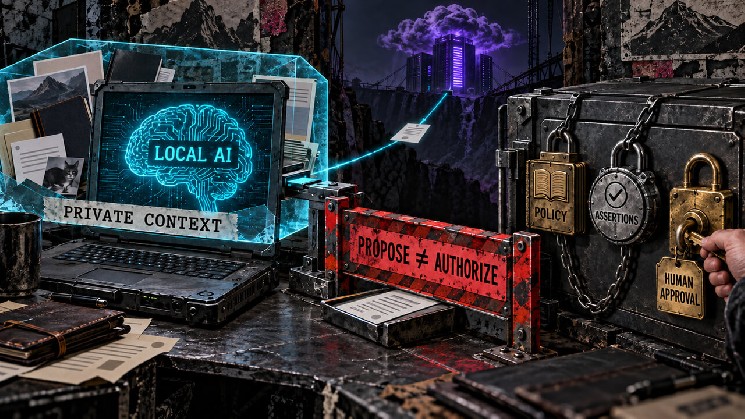
- Despite advances in local inference for privacy and responsiveness, Buterin and the Ethereum ecosystem maintain that crypto wallet authority must remain behind separate, enforceable controls—including human confirmation, deterministic policy limits, and emerging standards like EIP-7906.
Local AI Reaches New Practical Threshold on Consumer Hardware
Ethereum co-founder Vitalik Buterin declared on September 17 that recent improvements in llama.cpp and the release of Qwen 3.8 Flash have brought local large language models close to handling a “large share” of tasks on his Strix Halo laptop. The assessment marks a notable shift from his April evaluation, when he characterized laptop-bound models as limited to transcription, summarization, and other tightly bounded work. In the newer description, a local model can serve as the primary interface for a broader range of activity, coordinating requests to stronger remote systems while withholding the user’s full personal context.
Benchmark Data Quantifies Responsiveness Gains
An attached benchmark image detailed 10 workloads with reported input-processing rates ranging from 109.82 to 373.22 tokens per second and output generation from 18.42 to 33.37 tokens per second. Those figures support a practical claim about responsiveness on a single high-end device, though they leave critical questions—model judgment, resistance to malicious instructions, and transaction authorization—unanswered. Qwen3.8-Flash-Next, released by Alibaba‘s Qwen team, is an open-weight multimodal mixture-of-experts model with 125 billion total parameters, 51 billion in n-gram embedding tables, and 6 billion activated per token. Activating only a fraction of the model per token lowers the compute burden, though the official repository documents no single hardware minimum applicable across quantization levels and workloads.
Wallet Security Architecture Demands Layers Beyond Model Capability
While local inference improves privacy by keeping context on-device, Buterin emphasized that the power to move funds must remain behind separate, enforceable controls. Qwen’s technical report evaluates the base model across 14 benchmarks covering general knowledge, mathematics, science, reasoning, coding, and multilingual understanding—finding Flash-Next beat the larger Qwen3.7-Plus on eight tests—but prompt-injection resistance, policy enforcement, wallet authorization, and the correctness of autonomous financial actions fall outside that benchmark set. In his April wallet guidance, Buterin placed authorization policy outside the language model, describing a human-confirmation firewall for risky actions, deterministic limits on transaction amounts, calldata, and counts, and a human-plus-model 2-of-2 rule: “model may recognize a scam pattern that a distracted person misses, while a person may reject an action after malicious content manipulates the model. Requiring both approvals for risky transactions prevents either participant from quietly becoming the sole trust anchor.”
Ecosystem Experiments with On-Device Assistants and Post-Transaction Assertions
The Ethereum Foundation‘s second-quarter allocation update listed Steward, a fully local macOS smart-account wallet whose light client and AI assistant are intended to run on-device. The disclosure establishes funding and project scope but leaves production deployment, independent audit status, and autonomous transaction authority unestablished. Separately, EIP-7906 (still a draft) proposes post-transaction assertion frames that inspect final state differences produced by a transaction, allowing a wallet to require that a swap changed only approved balances, that a hidden token approval never appeared, or that a protected account’s state stayed untouched. Local inference and transaction assertions solve different parts of the wallet-agent problem: the local model protects context and turns natural-language intent into a proposed action; deterministic permissions restrict recipients, contracts, value, and frequency; assertions inspect final state changes; and human confirmation remains the second factor for risky actions.
Why This Matters
The convergence of high-throughput local inference on consumer hardware and evolving wallet security standards signals a maturing approach to AI-crypto integration. Buterin’s updated assessment reflects real progress in model efficiency—mixture-of-experts architectures like Qwen3.8-Flash-Next make meaningful local computation feasible without full-model activation—yet the Ethereum ecosystem’s cautious stance on asset authority underscores a deliberate separation between interface capability and trust-minimized control. Projects like Steward and proposals like EIP-7906 represent complementary layers: on-device assistants for privacy-preserving planning and monitoring, and cryptographic assertions for enforcing invariant rules that no model—local or remote—can override. For developers and users, the takeaway is clear: local AI can now credibly serve as a daily driver for information processing and transaction preparation, but the authorization boundary for irreversible asset movements remains firmly anchored in deterministic code and human intent.
Frequently Asked Questions
- Can a local AI model like Qwen 3.8 Flash autonomously control crypto assets on a laptop?
- No. Buterin and the Ethereum ecosystem explicitly maintain that wallet authority must remain behind separate, enforceable controls—including deterministic policy limits, human confirmation for risky actions, and cryptographic assertion frames (EIP-7906). The model serves as an interface, planner, and monitor, not a trusted signer.
- What hardware is needed to run Qwen 3.8 Flash locally at the reported speeds?
- The benchmarks were recorded on a Strix Halo laptop. Qwen3.8-Flash-Next uses a mixture-of-experts architecture with 6 billion parameters activated per token (125B total), and the official llama.cpp GGUF builds support quantized inference. The Qwen team documents no single hardware minimum; requirements vary by quantization level, context length, and workload.
- How does the September assessment differ from Buterin’s April view?
- In April, Buterin wrote that Qwen3.5:35B could handle bounded tasks and familiar programming work, while advanced independent agents that could keep working on a codebase remained beyond laptops’ practical reach. Harder coding and intellectual work still called for stronger remote models. By September, he describes the local model as a main interface for a “large share” of activity that selectively routes to remote systems, acting as both an information gatekeeper and an assistant.
